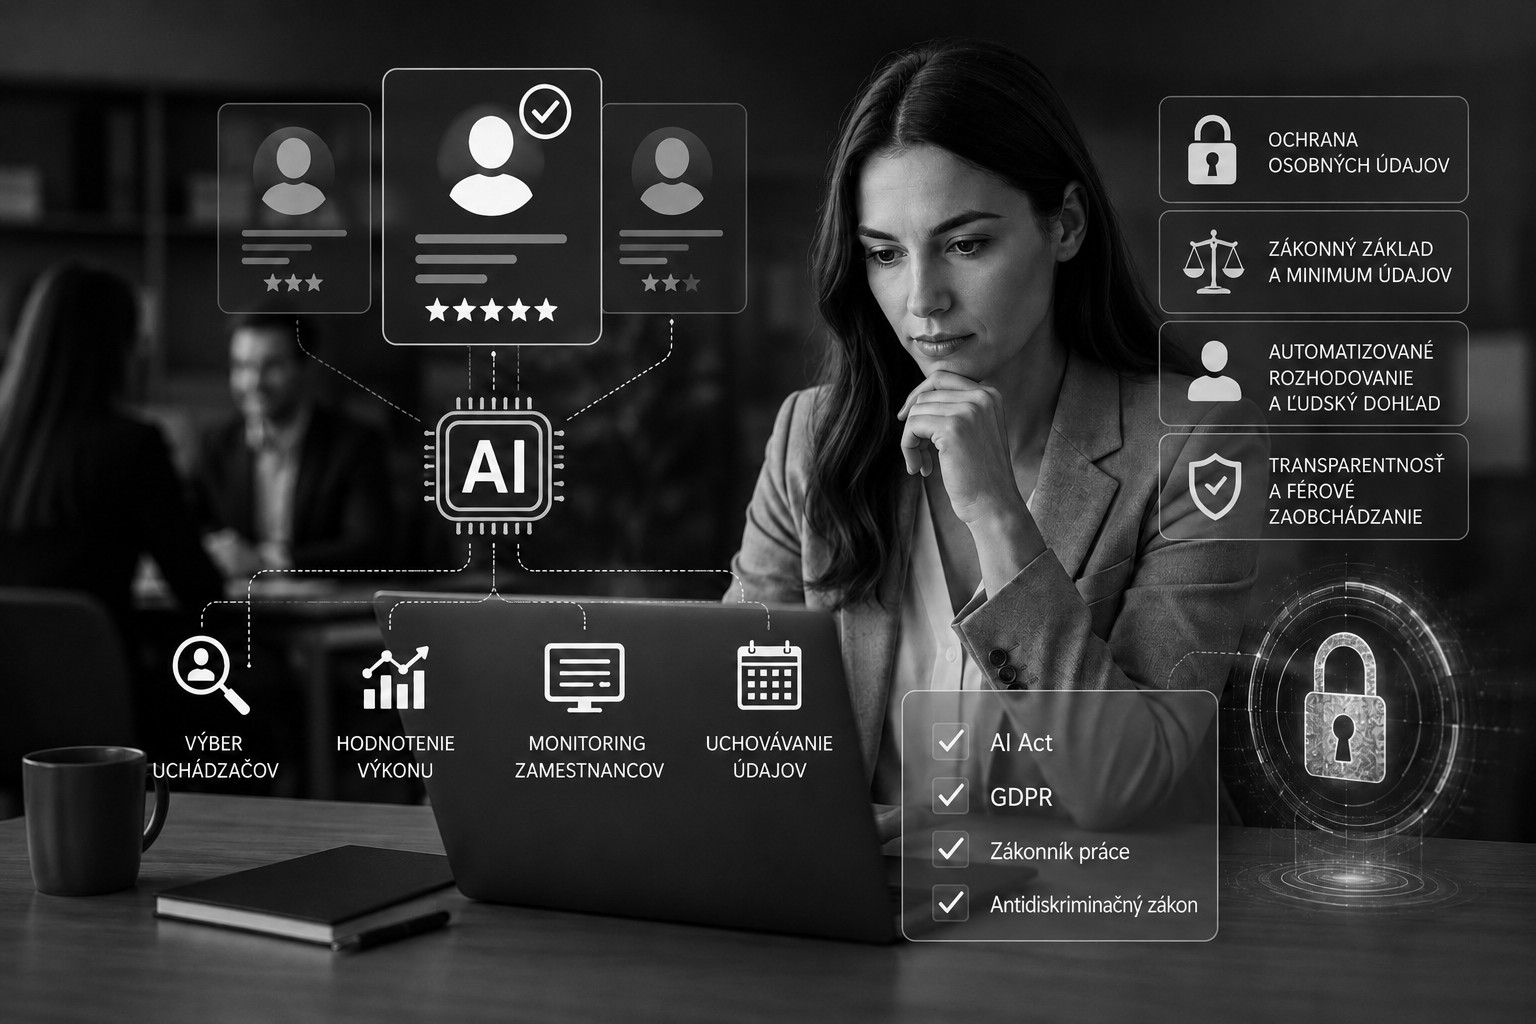
Today, an AI tool can read hundreds of CVs within minutes, score candidates, recommend who should be invited to an interview, or alert a manager to a decline in productivity. This is precisely why artificial intelligence in HR is not merely a technological issue. Every such output may affect a person’s access to employment, working conditions, remuneration, employment relationship, or even the termination of employment. A single process may therefore involve the AI Act, the GDPR, data protection rules, the Labour Code, anti-discrimination legislation and the employer’s internal policies.
The first rule is not to assess a tool by its name, but by what it actually does in practice. A calendar that merely suggests an interview time presents a different level of risk from a system that filters CVs, evaluates personality, predicts job performance or assigns tasks to employees. What matters is which personal data the system processes, whether it profiles individuals and to what extent its output actually influences an HR or managerial decision.
AI in Recruitment: An Assistant, Yes — an Invisible Decision-Maker, No
AI may be used in recruitment to identify relevant experience, sort CVs, compare qualifications with job requirements or prepare supporting information for a recruiter. Systems intended for the recruitment and selection of employees, particularly those used to analyse and filter job applications or evaluate candidates, are among the typical high-risk uses under the AI Act. The same applies to tools used to make decisions on promotion, termination of employment, allocation of tasks based on behaviour or personal characteristics, and monitoring or evaluation of employee performance. Following the amendment of the AI Act through the Digital Omnibus, the key rules governing these stand-alone high-risk systems will apply from 2 December 2027.
This does not mean, however, that HR is unregulated until then. The GDPR, employment law and the prohibition of discrimination already apply today. In addition, the prohibited practices under the AI Act also apply, including, for example, the use of AI to infer emotions in the workplace from biometric data, except for narrowly defined medical or safety-related reasons. A video interview therefore cannot be turned into an automated test of nervousness, honesty or emotional stability merely because a supplier offers such functionality.
Section 41 of the Labour Code also applies to recruitment: an employer may request only information related to the job and may not use an algorithm to circumvent prohibited questions. If a recruiter is not allowed to ask about pregnancy, family circumstances, political affiliation, trade union membership or religious beliefs, AI should not indirectly infer them from a photograph, name, address or career history either.
GDPR: Legal Basis, Data Minimisation and a Clear Retention Period
Every CV, test result, interview note, employee performance evaluation, attendance record or GPS location constitutes personal data if it can be linked to a specific individual. As the controller, the employer must determine, for each purpose, the legal basis, the scope of the data, the recipients and the retention period. Consent to the processing of personal data is not a universal solution.
In employment relationships, the voluntary nature of consent is often problematic, and during recruitment the processing may be necessary in order to take steps prior to entering into an employment contract or may rely on another appropriate legal basis depending on the specific purpose.
The GDPR transparency obligation should be practical, not hidden in a lengthy document. A candidate or employee should know what data the system uses, where the data comes from, what the system derives from it, to whom the data is disclosed and how long it is retained. The principle of data minimisation means that a company should not collect everything that it is technically capable of collecting. The retention period must correspond to a genuine purpose: the data of an unsuccessful candidate should not automatically be transformed into a permanent talent profile, and monitoring data from work devices should not be retained indefinitely.
Where more extensive profiling, systematic evaluation of individuals or monitoring is involved, the need for a DPIA — a data protection impact assessment — should be assessed. In cases involving automated evaluation with significant effects, the GDPR may expressly envisage the need for a DPIA. The assessment should be carried out before the system is deployed, not only after an employee submits a complaint.
Automated Decision-Making and Genuine Human Oversight
The most sensitive line is crossed when the system effectively makes the decision itself. The GDPR protects individuals against decisions based solely on automated processing, including profiling, where such decisions produce legal effects or similarly significant effects. Automatic rejection of a job applicant, denial of a promotion or imposition of a sanction may reach this threshold.
Human oversight must be genuine. It is not sufficient for a manager to click “approve” without understanding the criteria, reviewing the underlying information or being able to change the recommendation. The person carrying out the review must have the competence, training and authority to challenge the system.
Following the amendment, the AI Act requires providers and deployers of AI systems to take measures to support the AI literacy of people working with such tools. Employee training and GDPR training should therefore explain not only how to operate the system, but also its limitations, the risk of bias, data protection requirements and the procedure to follow when the system produces an incorrect output.
Monitoring Productivity, Emails, Devices and GPS
Employee monitoring is an area where technical possibilities meet the limits of privacy. Section 13 of the Labour Code does not allow an employer, without serious reasons arising from the specific nature of its activities, to interfere with an employee’s privacy by monitoring them, recording work-related telephone calls or inspecting work emails without prior notice.
Where a monitoring mechanism is introduced, its scope, method and duration must be discussed with employee representatives, and employees must be informed about it.
Proportionality must be assessed in light of the purpose. Logging access to a system for cybersecurity purposes is different from analysing the content of every message, the number of clicks or mouse movements as evidence of work performance.
With GPS monitoring, it is necessary to distinguish between protecting a vehicle or organising working time and continuously tracking a person outside working hours as well. Appropriate safeguards may include limiting monitoring to the necessary period, precisely defining the authorised persons, applying a shorter retention period and providing a technical option to disable monitoring outside working hours where the purpose permits.
Who Is Responsible: the Employer, the Supplier or the User?
Responsibility cannot be resolved by a single clause in terms and conditions. Under the GDPR, the employer will generally be the controller because it determines why the personal data of candidates and employees is used.
The supplier may be a processor if it processes data solely on the employer’s instructions, but if it uses the data for its own model training or for its own purposes, it may have an independent role.
Under the AI Act, the manufacturer or supplier of the system will typically be the provider, while the company using the tool will be the deployer. However, if the company substantially modifies the system, markets it under its own name, or changes its intended purpose in a way that creates a high-risk use, it may assume the obligations of a provider.
A data processing agreement should address instructions, security, sub-processors, incidents, transfers to third countries and data deletion. The commercial agreement should additionally regulate the accuracy and limitations of the tool, model changes, logging, audits, explainability of outputs, testing for discriminatory effects and cooperation in connection with a candidate’s request or a regulatory inspection.
The supplier is not a legal shield: the employer’s rights and obligations remain in place even when the tool is provided as a cloud service.
Discrimination and Bias: Review the Results, Not Just the Model
AI may reproduce historical decisions or rely on proxy variables that appear neutral at first glance. A person’s address, school, language, length of a career break or type of working arrangement may result in indirect discrimination if they disadvantage a particular group without an objective and proportionate justification.
The review should therefore not end with the supplier’s declaration of compliance.
The company should regularly compare whom the system recommends, whom it excludes and which groups show significant disparities. The criteria must be relevant to the job, understandable and capable of being reviewed.
When dealing with persons with disabilities, reasonable adjustments to testing must also be considered. If sensitive personal data must be processed in order to test for bias, there must be a specific legal basis and strict safeguards. Such data cannot be collected merely because doing so would be analytically interesting.
What an Internal AI Policy for HR Should Include
A good internal policy or updated workplace rules should establish a simple process from the purchase of a tool through to its everyday use.
It should define an AI systems register, permitted and prohibited uses, responsible persons, the legal basis for processing, data minimisation and retention rules, human oversight, discrimination testing, DPIA requirements, incident procedures and the conditions applicable to employee monitoring.
It should also contain rules on when public generative AI tools may be used and which personal data or trade secrets employees must not enter into them.
Internal policies must reflect actual practice. If a document states that AI merely provides assistance, but managers always adopt its scores without question, the company is effectively engaging in automated decision-making, regardless of what the policy says on paper.
If the GDPR documentation specifies a short retention period, the system must be technically configured to actually delete the data. And if training refers to human oversight, the user must have sufficient time, information and authority to make a different decision.
Carry Out a Simple Legal Assessment Before Deploying AI
Before purchasing or activating a new AI function, HR, IT, legal counsel and the Data Protection Officer should be able to answer several basic questions:
What is the precise purpose of the system? Which personal data does it genuinely need, and which data does it merely collect in addition? Does it carry out profiling? Does it affect recruitment, remuneration, working conditions, working time, promotion or termination of employment? Who can override its recommendation? What logs are generated and how long are they retained?
If the company cannot answer these questions, its transparency information, internal policy and supplier agreement are not ready either.
It is equally important to review what happens after deployment. The employer’s obligations do not end when the contract is signed. Changes to the model, new functions, the accuracy of outputs and user complaints must continue to be monitored.
If a tool originally intended to provide administrative assistance gradually becomes a system used to evaluate employee performance, its purpose, risk classification, legal basis and DPIA must be reassessed.
Internal policies should therefore introduce regular reviews and an obligation to notify HR or the DPO of any change before it is activated. This helps ensure that GDPR documentation, workplace rules and the actual rights and obligations of employees do not diverge from what the technology is really doing.
AI in HR can accelerate recruitment, simplify work organisation and assist with the evaluation of large volumes of data. A legally sound model, however, rests on four pillars: a clearly defined purpose, lawful processing of personal data, appropriate human oversight and evidence that the system does not produce discriminatory or disproportionate outcomes in practice.
When these rules are properly reflected in contracts, GDPR documentation, internal policies and employee training, artificial intelligence can become a useful HR tool without turning into an invisible decision-maker over a person’s working life.